OWASP API Security Top 10: What a linter can see in your OpenAPI document
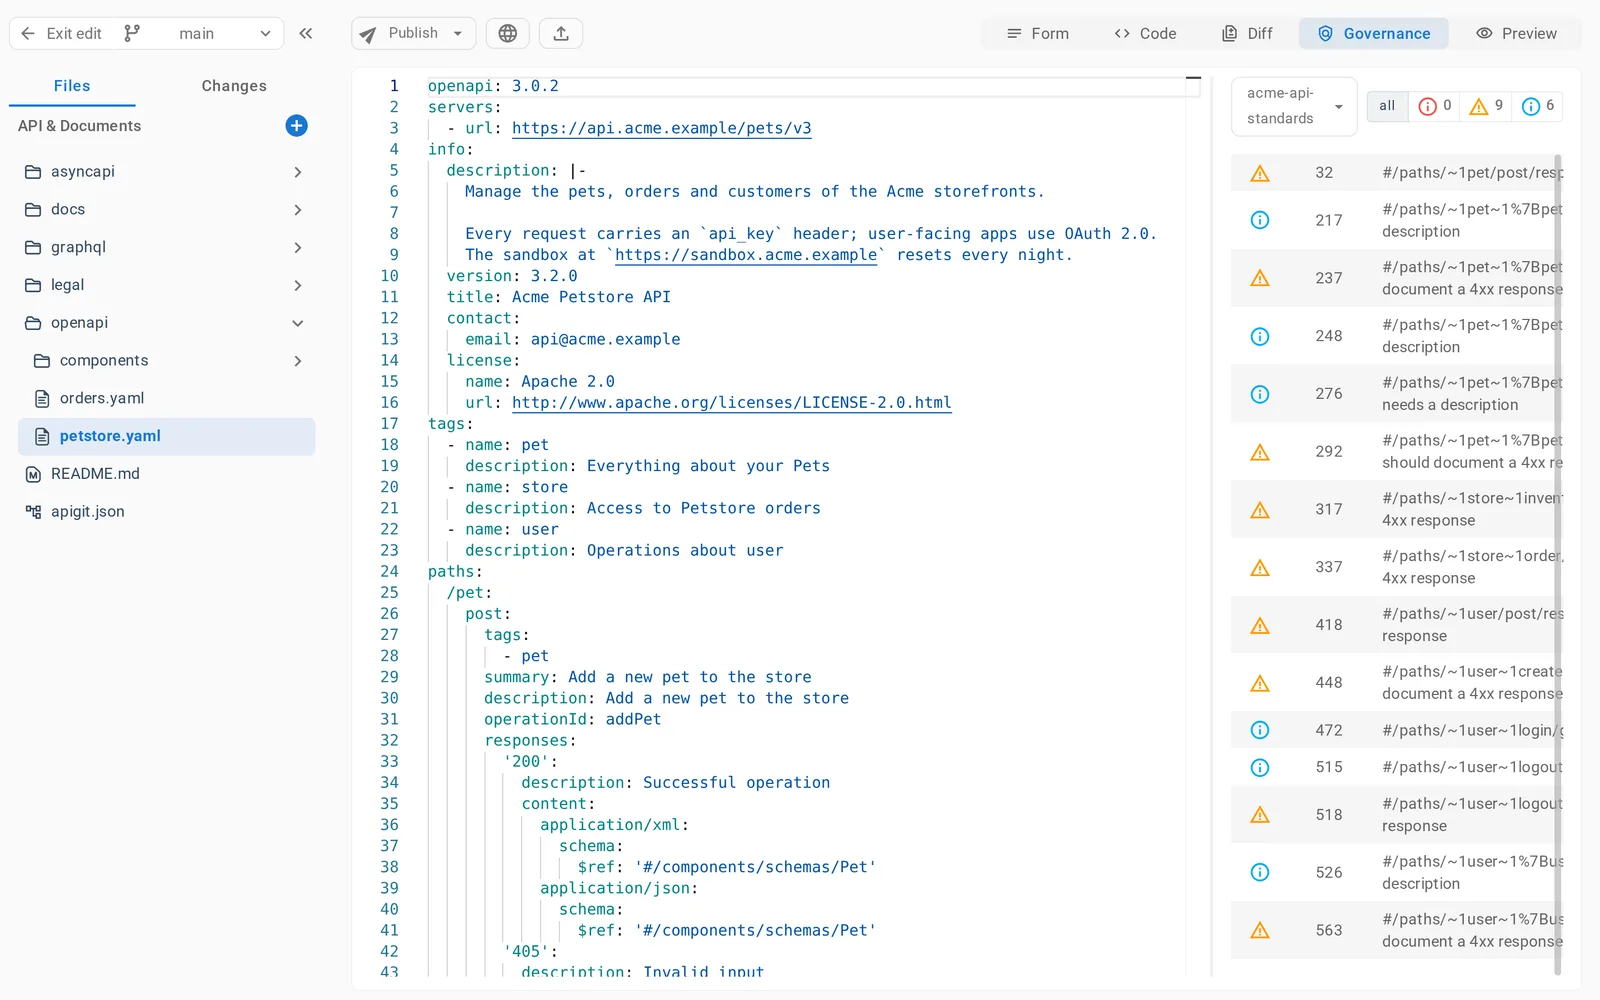
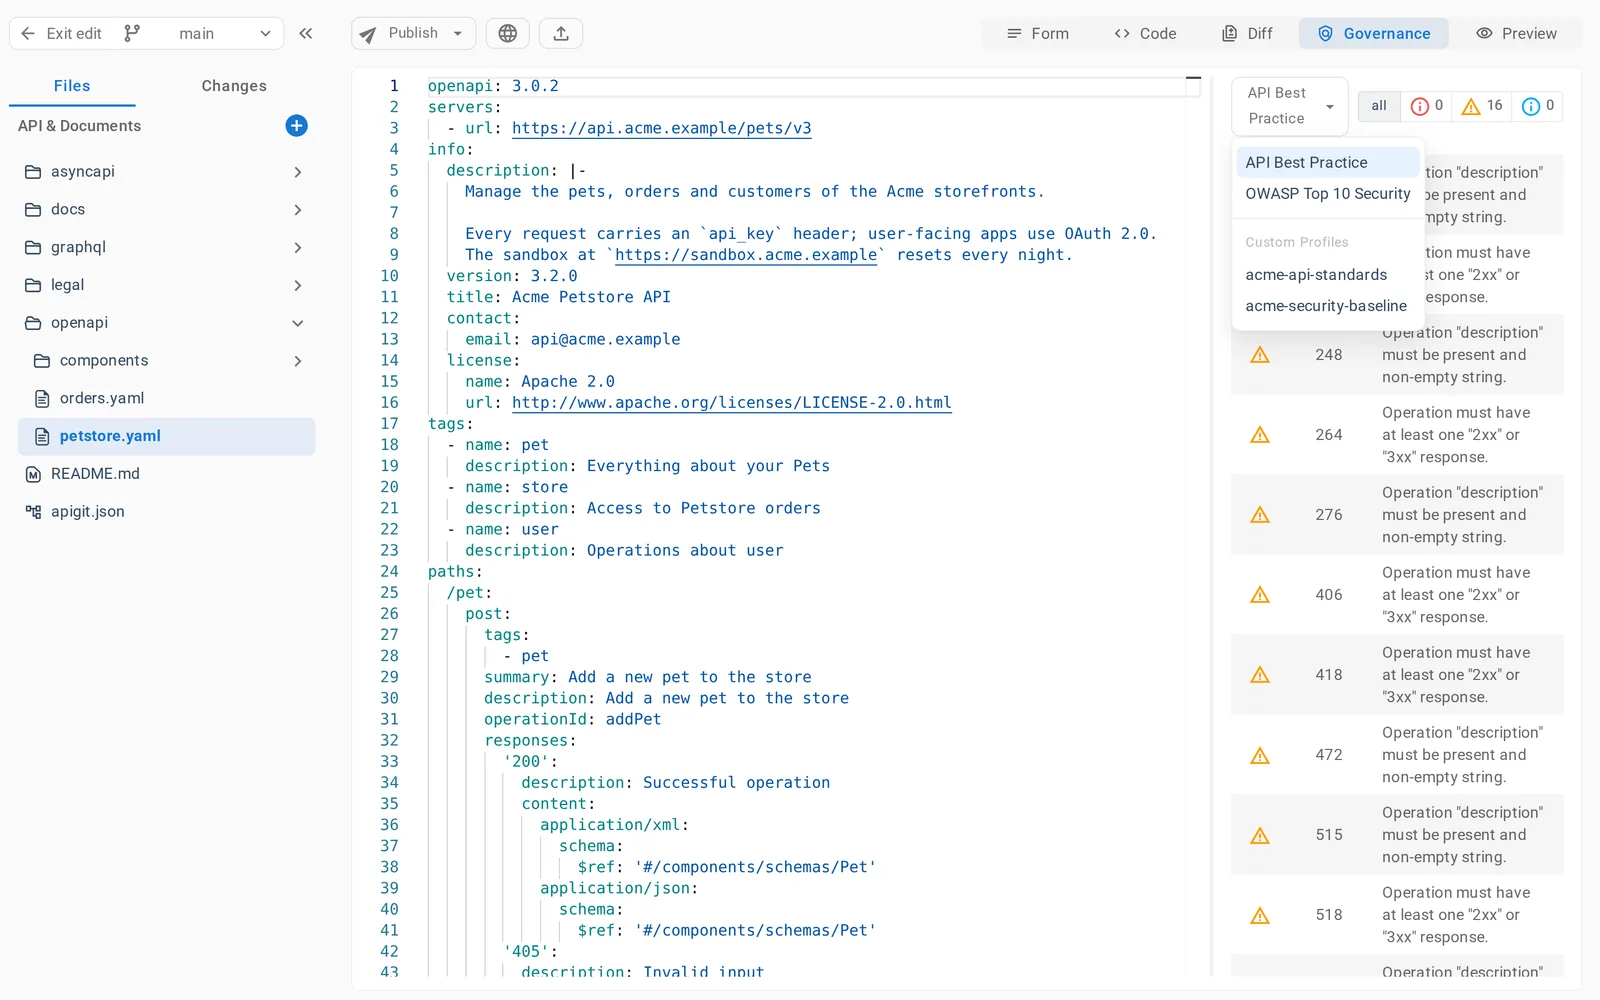
Eight of the ten OWASP API risks leave a trace in the contract. For each risk: what the OWASP rule set checks in an OpenAPI document, what it cannot see, real findings on a small example, and how to adopt it without drowning.